Hellspin: Vergleich der beliebtesten Glcksspiele
12/06/2026Dlaczego gracze wybierają gry na żywo i jak Marvel Casino ułatwia kontakt z krupierem
13/06/2026The SSL/TLS HostnameVerify process is(CWE-295)not applied appropriately in some apps, allowingcertificates with incorrect or mismatched hostnames to beaccepted. This can lead to data breaches.Certificate chain checking ensures the validity of SSL certificatesAn attacker needs to be in a MiTM position toBad certificates chainpresented by the server when communicating with the app. Developers often hard-code this key into thetransmitted utilizing the appliance or device.app code.The initialization vector is used to randomize ciphersince the same inputs outcome in the sameUse of statictexts with the identical input.
Hardcoded Authentication Tokens
Utilizing PCI-compliant cloud HSMs, it simplifies payment infrastructure and helps scale back PCI scope, whereas providing full help for issuer Certificates Authority (CA) features and secure PIN workflows. Banks depend on 1000’s of cryptographic keys across ATMs, mobile apps, card techniques, and backend infrastructure. Managing these keys securely — with central control, policy enforcement, and full lifecycle auditing — is a significant operational and compliance challenge.
- 2, the ten most common SRCSs within the WAEMU banking apps affect between 20 to 80% MBAs.
- Those functions are referred to as cellular banking functions or cell banking apps (shortly MBAs here).
- We recognize your time reviewing and reporting rendering errors we may not have discovered yet.
- Unsuspecting users who sideload these fraudulent apps expose their credentials and sensitive knowledge.
- This permits them to obtain two-factor (2FA) codes and reset your banking credentials.
Cellular Banking Application?
Image a hacker stealing one password and accessing a person’s bank data in comparability with a hacker that would want to present a selfie, a password, and voice authentication to access the same information. Biometrics uses a person’s physical traits – face, voice, fingerprint, and so on. A particular person could mix up or overlook their password, but their face stays their face. Uncover the technical controls examiners count on and tips on how to https://joomline.net/ru/forum/jlcomments/6060-jl-comments-pro.html automate them at construct time. Quokka has solutions that provide deep evaluation and visibility required to stay forward of cell threats.
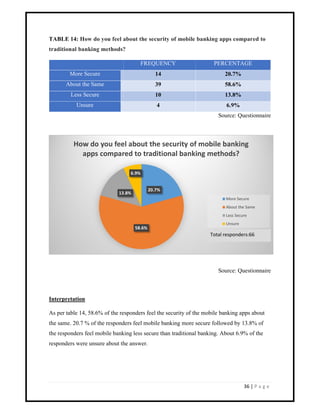
If you’re ever unsure or need help, your bank’s customer support staff is just a cellphone name or click away. Creating a safe mobile banking ecosystem requires a proactive and collaborative approach. Customers should stay vigilant and informed about potential threats, while financial institutions have to prioritize complete safety measures and continuous improvement. As emerging technologies like AI, blockchain, and behavioral biometrics evolve, they offer promising solutions to boost safety and person expertise. By combining these tools with consumer schooling and robust insurance policies, we will foster a future where cellular banking isn’t solely handy but also extremely safe for everybody. Varied approaches have been explored to assess the safety problems with cellular banking apps, ranging from investigating their origins 6 to conducting forensic examinations and vulnerability assessments 7, 8.
Four Baby And Parent Banking Apps
Nonetheless, there remains a niche in analysis addressing these issues comprehensively. At least half of the EU, US, and ODC banking apps use hard-coded passwords to derive a cryptography key, which is then used to encrypt and decrypt data. Such behavior is more advanced than directly hard-coding the key however leads to the same vulnerability. In 20% of the WAEMU apps, this key is immediately hard-coded, avoiding the key derivation step.
This work assesses the safety of MBAs from financial institutions in the WAEMU countries. This part describes the Analysis Questions (RQs) and the app collection and analysis process. Dangerous protocol verifier (34%).SSL/TLS protocol protects the app’s knowledge by encrypting the connection between the consumer and server.If protocols thought-about insecure, corresponding to SSL(v1), SSLv2, SSLv3, TLSv1, and TLSv1.1, are used, this could make connections vulnerable to exploits. Vulnrability for breach attack (41%).This is expounded to HTTP compression.If an app allows compression for an HTTP(s) connection when transferring sensitive information, an attacker can get information about the corresponding response by simply injecting plaintext into the request. To higher perceive the security implications of these findings, we manually analyzed the apps’ source code.This handbook examination facilitated the institution of potential real-world assault vectors for exploiting the identified vulnerabilities.
Developers should defend this knowledge both at the client-side and the back-end. This contains secure communication between your consumer and the back-end. You may also want to ensure any information in memory stays there for as restricted a time as attainable and is properly protected. Whereas banks employ a number of fraud prevention tools, similar to secure SDKs, multi-factor authentication (MFA), and Know-Your-Customer (KYC) protocols, these measures are not foolproof. Scammers might exploit SIM swapping, where they trick your cell provider into transferring your telephone number to a new SIM card. This permits them to obtain two-factor (2FA) codes and reset your banking credentials.